

Companies deploying artificial intelligence today face a seemingly simple choice: on-premise or cloud. On-premise gives full control but requires owning and maintaining your own infrastructure. The cloud is flexible and scalable, but it means handing your data over to a third-party provider - even one that claims the highest security standards.
Between these two extremes there's a third path: TEE, or Trusted Execution Environment. This technology lets you run AI models and process data in the cloud in a way that keeps it out of reach even for the administrators of the infrastructure the system runs on. In this article, we explain exactly what TEE is, how it works, and why it's becoming an increasingly important part of secure AI deployments in business.
What is a Trusted Execution Environment (TEE)
A Trusted Execution Environment is an isolated execution environment, carved out at the hardware level of the processor, where data and program code are processed in a way that's cut off from the rest of the system - including the operating system, the hypervisor, or the cloud provider itself. In practice, this means that even if someone gains full administrative access to the machine running the TEE, they still can't read the data or code being processed inside that enclave.
TEE relies on memory encryption and hardware isolation mechanisms built directly into the processor. The best-known implementations of this technology include Intel SGX and TDX, AMD SEV, and ARM TrustZone - used today by major public cloud providers as part of what's known as confidential computing.
This is what sets TEE apart from standard encryption of data "at rest" and "in transit," which protect data while it's stored on disk or moving across a network, but not while it's actively being processed in the processor's memory. TEE closes that gap - it provides encryption and isolation for data in use as well.
How TEE protects data in AI systems
In the context of AI deployments - especially large language models (LLMs) and RAG systems that draw on a company's internal knowledge - TEE addresses three specific risks:
Protection from the infrastructure provider. Even in a private cloud, data could theoretically be read by an infrastructure administrator, due to a misconfiguration, a security flaw, or malicious code running at the hypervisor level. TEE removes this scenario entirely, since data inside the enclave is inaccessible even to the layer managing the virtual machine.
Protection of the model and its weights. Companies that invest in fine-tuning their own language model want to protect not just the input data, but the model itself - its weights and parameters, which represent real intellectual property. TEE allows inference to run in a way that keeps the model encrypted and inaccessible for copying or analysis by third parties.
Verifiability of the environment (remote attestation). TEE enables what's known as remote attestation - a process through which a company can cryptographically verify that its data is genuinely being processed inside a certified, untampered enclave, rather than in an ordinary, unsecured environment. That's real proof of compliance, not just a vendor's claim.
TEE vs. On-premise and Standard private cloud – key differences
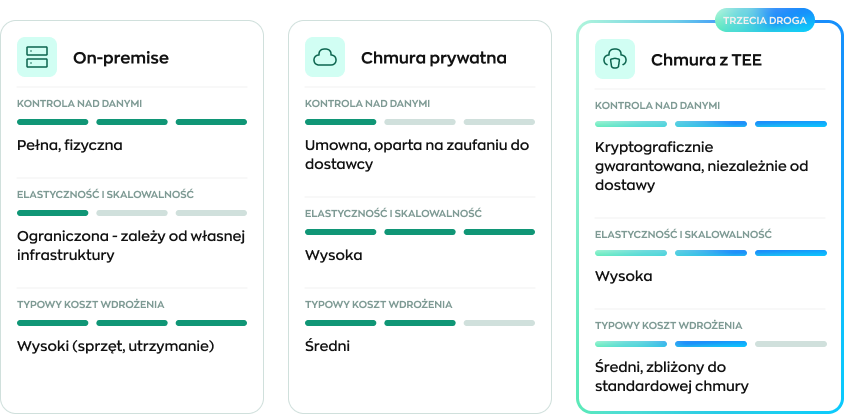
For many companies, TEE is the optimal middle ground: it lets them keep the flexibility and cost profile of the cloud while achieving a level of data isolation close to an on-premise environment - without having to build and maintain their own data center.
When to consider AI deployments built on TEE
TEE matters most where the data processed by an AI system is particularly sensitive or subject to strict regulatory requirements:
- financial services – transaction data, credit risk assessments, customer data covered by banking secrecy,
- automotive and manufacturing – technical documentation and data subject to TISAX requirements,
- healthcare – patient data subject to special legal protection,
- law firms and advisory businesses – documents covered by professional secrecy and confidentiality clauses,
- technology companies protecting their own AI models – when the model or training data represents a key competitive advantage.
In practice, if a company finds itself asking, "can I trust my cloud provider enough to hand over this data with no reservations at all" - and the answer is "not entirely" — that's a sign it's worth considering a TEE-based architecture.
What deploying an AI system in a TEE environment looks like
Deploying this type of solution differs from a standard integration with a public AI model API. It requires:
- Auditing data and regulatory requirements – identifying which processes and datasets actually need the level of protection TEE offers, and which can run on a simpler architecture.
- Choosing a cloud provider and processor that support confidential computing – not every cloud service, and not every region, offers TEE support.
- Preparing the application and model to run inside the enclave – this includes properly configuring the runtime environment and, where needed, adjusting how the model is loaded.
- Implementing a remote attestation mechanism – so the company can continuously verify the integrity of the environment, rather than simply trusting the provider's word.
- Security and performance testing – processing inside an enclave carries some performance overhead, which is worth measuring and optimizing before going to production.
Summary
TEE is one of the few technologies that genuinely closes a real gap in AI data protection - not just when data is stored or transmitted, but also while it's actively being processed by a model. For companies that want the flexibility of the cloud but can't afford to give up control over sensitive data or their own AI model, TEE is today one of the most credible solutions - combining on-premise-level security with cloud-level scalability.
Wondering whether your company needs a TEE-based architecture? Check out our AI & Cloud audit, where we assess which environment best fits your data security requirements, or explore our Secure RAG Systems built for full isolation of your company's knowledge. You can also book a free consultation.